Why Healthcare Compliance Failures Happen — and How Workflow Automation Helps Prevent Them
Healthcare organizations invest heavily in policies, security tools, and training. Compliance can still fail when everyday operational controls are executed inconsistently: access is not revoked, incidents are not routed, approvals are skipped, or the audit trail depends on someone remembering to document what happened.
Healthcare compliance failures are not one problem with one fix. Cyberattacks remain the dominant source of large HIPAA breaches, while HHS investigations repeatedly identify weaknesses in risk analysis, risk management, system activity review, audit controls, and authentication. Workflow failures create a different but connected risk: even with good policies and security products, controls can break when access reviews, offboarding, incident escalation, document handling, approvals, and evidence collection rely on people executing every step manually. Automation helps by turning those repeatable controls into governed, logged processes.
What’s in this guide
- The healthcare compliance challenge in 2026
- Where compliance execution breaks down
- Why identity and offboarding deserve special attention
- Four ways healthcare teams address compliance risk
- Why workflow automation closes a different gap
- Healthcare compliance automation in Google Workspace
- More on Google Workspace compliance

The healthcare compliance challenge is getting harder, not simpler
Healthcare cybersecurity is both a technology problem and an operating-model problem. Organizations need to defend systems against increasingly capable attackers while also proving that the policies designed to protect protected health information (PHI) are being followed in day-to-day work.
The latest annual breach report available from the U.S. Department of Health and Human Services (HHS) makes the threat landscape clear. HHS Office for Civil Rights (OCR) recorded 663 large breaches that occurred in 2024, affecting approximately 242.9 million individuals. Hacking and IT incidents represented 81% of large reported breaches. At the same time, OCR highlighted risk analysis, risk management, system activity review, audit controls, and authentication as recurring areas where regulated entities need to improve. See the HHS breach reports.
HHS enforcement activity in 2026 reinforces that point. By June 2026, OCR had announced its twentieth ransomware enforcement action and fourteenth enforcement action under its Risk Analysis Initiative. OCR continues to emphasize safeguards such as risk analysis, access controls, system review, encryption where appropriate, and workforce-specific training. See the June 2026 OCR enforcement notice.
Where healthcare compliance processes break down
Policies describe what should happen. Operational workflows determine whether it actually happens — on time, for the right person, with the correct approvals and evidence.
Access is granted inconsistently, revocation is delayed, or an application is missed because the process depends on separate administrators remembering separate steps.
A privacy or security concern is reported, but the correct owner, deadline, documentation, or escalation path is not consistently triggered.
Sensitive data accumulates in shared drives, folders, mailboxes, or SaaS applications while permissions outlive the business reason for access.
The organization performed the right action but cannot easily reconstruct who approved it, when it happened, what changed, or which exception was accepted.
Approvals, follow-ups, reminders, and supporting evidence are scattered across inboxes rather than captured in a controlled process.
Staff copy data between forms, spreadsheets, EHRs, CRM systems, Drive folders, and email — increasing the number of opportunities for mistakes and inappropriate exposure.
The common denominator is not that employees are careless. The problem is that a process which depends on perfect human execution every time will eventually produce exceptions. Compliance teams need people for judgment; they should not need people to remember every repetitive control step.
Offboarding shows how a small execution gap can become a security problem
User lifecycle management is a good example because the policy is rarely ambiguous: when an employee or contractor leaves, access should be removed according to the organization’s rules. The execution can still span Google Workspace, shared files, groups, third-party applications, delegated mailboxes, licenses, and other systems.
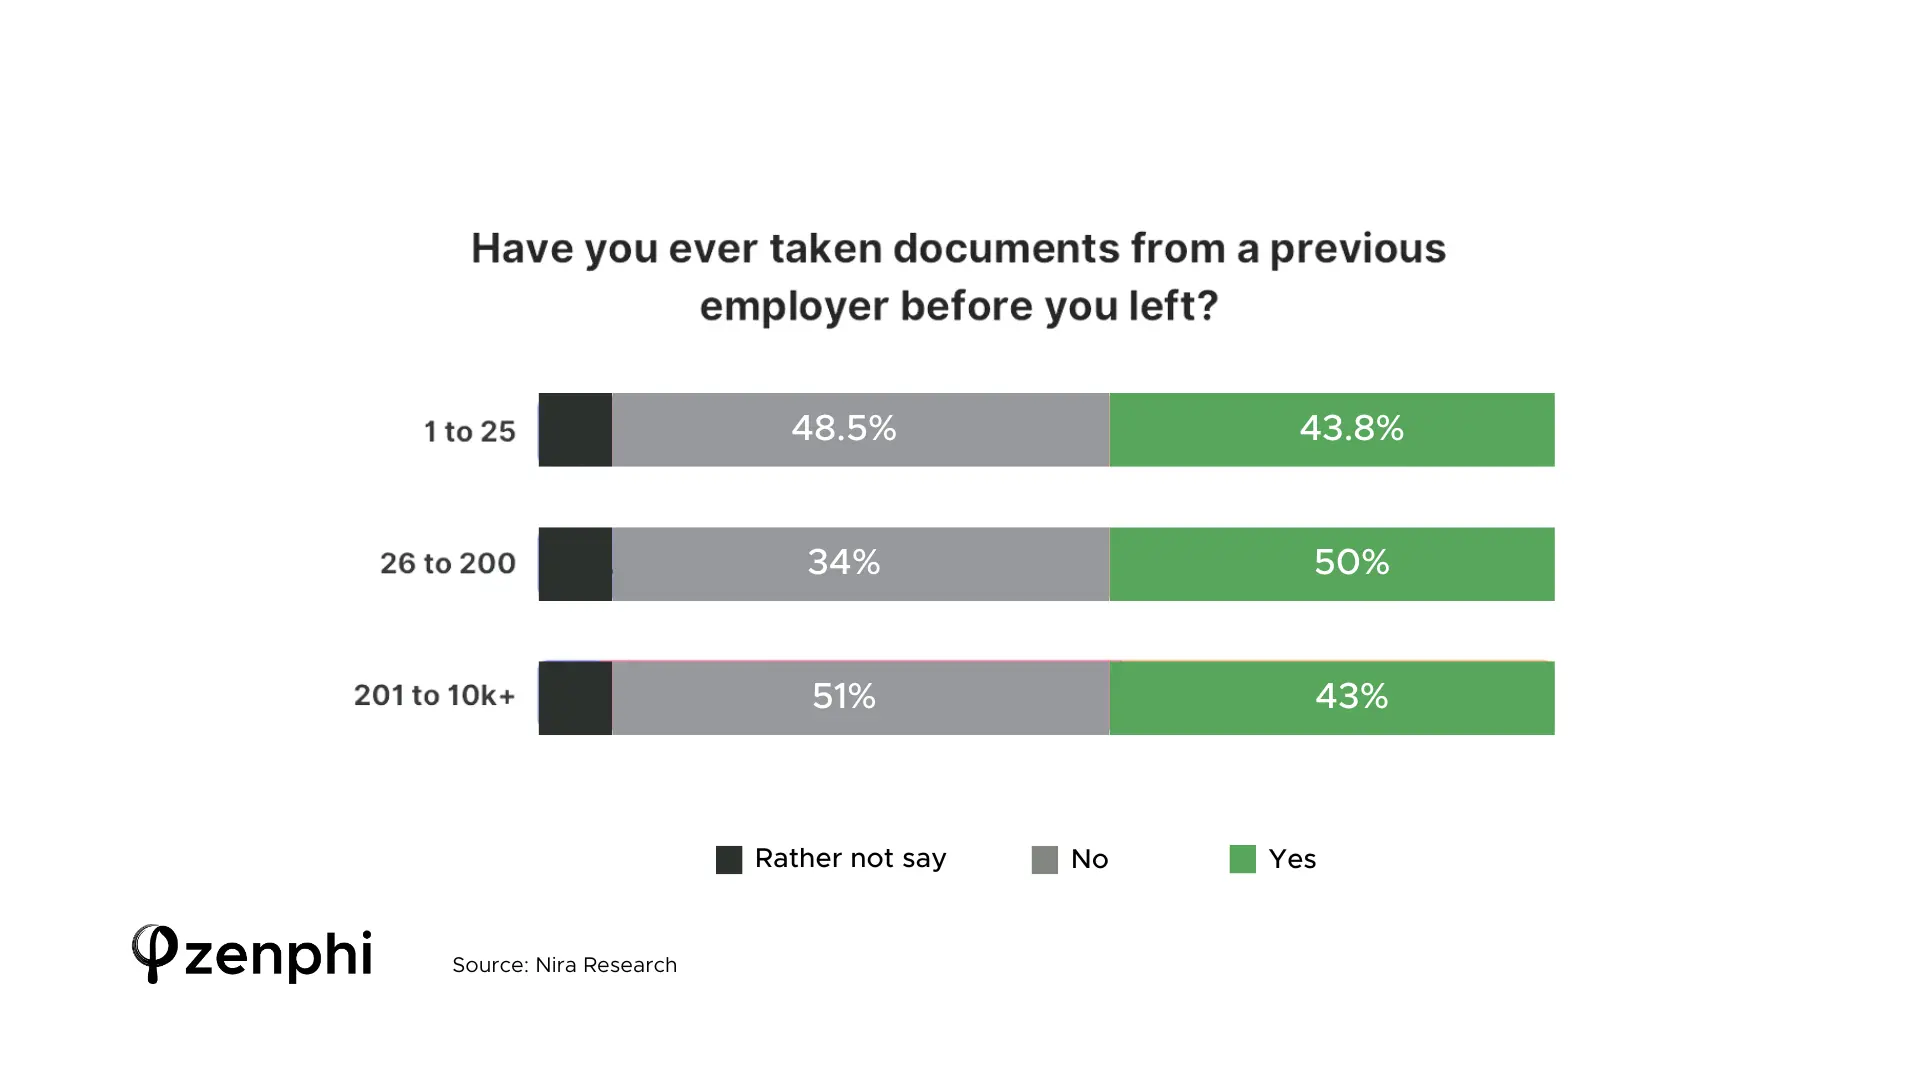
Instead of making offboarding a checklist that several teams must coordinate manually, a governed workflow can turn the approved termination event into a sequence of actions:
Start from HR, a controlled form, or another authorized source rather than an informal email request.
Look up the employee, manager, department, role, and any conditional handling required by policy.
Execute the Google Workspace and connected-system actions defined for that user rather than relying on separate manual tickets.
If an action fails, requires judgment, or needs an approval, route it to the correct person instead of silently leaving the process incomplete.
Record what happened, when it happened, and which human decision was made so compliance evidence is produced by the process itself.
Four ways healthcare teams address compliance risk
Training, compliance staff, security software, and workflow automation solve different parts of the problem. Mature healthcare organizations generally need all four in some proportion. The mistake is expecting one layer to compensate for gaps in another.
1. Manual checklists and training
Necessary foundationPolicies and training establish expectations and teach employees how to handle sensitive information. They remain essential, but they are weakest when a recurring operational control depends on a person remembering to execute and document every step.
- Low implementation cost.
- Fast to introduce.
- Easy to adapt to internal policy.
- Essential for judgment-based behavior.
- Dependent on human consistency.
- Hard to monitor in real time.
- Evidence may be manually assembled.
- Gets harder to enforce as process volume grows.
2. Additional compliance staff
Human oversightDedicated compliance professionals bring expertise, interpret changing requirements, review exceptions, investigate concerns, and establish accountability. That is high-value human work. Adding staff does not automatically repair the process they are overseeing.
- Specialized compliance expertise.
- Human judgment for ambiguous cases.
- Dedicated monitoring and remediation.
- Clear ownership of policy.
- Headcount is expensive to scale.
- Does not eliminate repetitive manual work.
- Experts can still be overwhelmed by volume.
- Process flaws remain process flaws.
3. Security software
Threat & control layerSecurity platforms are essential for identity protection, endpoint security, threat detection, monitoring, encryption, vulnerability management, and response. They reduce technical risk but are not designed to orchestrate every business process that has a compliance consequence.
- Detects threats and anomalous behavior.
- Enforces technical security controls.
- Improves incident visibility.
- Supports security monitoring and response.
- May require specialist implementation.
- Does not orchestrate every operational handoff.
- Cannot guarantee employees follow a business process.
- Security and operational workflow data may remain separate.
4. Workflow automation
Execution layerHealthcare workflow automation turns policies and repeatable operating procedures into executable processes. It does not replace security tools, compliance professionals, or employee training. It reduces the number of points where those controls depend on someone remembering the next step.
- Consistent routing and execution.
- Built-in reminders and escalations.
- Human approval gates where judgment is required.
- Execution history generated automatically.
- Workflows must reflect the correct policy.
- Permissions and integrations require governance.
- Exception paths must be designed deliberately.
- HIPAA obligations remain a shared responsibility.
Download the Google Cloud Cybersecurity Forecast 2026
Dive deeper into how operational weaknesses are being exploited — and what organizations need to prepare for next. Use the forecast as a discussion guide for your IT, security, and operations teams as you plan the controls and workflows that need strengthening.
Explore the 2026 forecast
Automation reduces the cost of inconsistency
The strongest case for automation is not that it makes an organization “compliant automatically.” It is that repeatable control steps can become predictable: the same trigger produces the same routing, the same approval requirement, the same escalation path, and the same evidence.
Required steps run as designed rather than varying according to who happened to handle the request.
Time-sensitive actions can happen immediately after the approved trigger rather than waiting for a manual handoff.
Actions, timestamps, approvals, and exceptions are captured as part of execution instead of reconstructed later.
Higher volumes do not require a linear increase in staff simply to perform and document repetitive control steps.
IBM’s 2026 Cost of a Data Breach research provides a related security benchmark: organizations using AI and automation extensively in security operations reduced breach costs by almost $2 million on average compared with organizations that did not. IBM’s finding is specifically about security AI and automation, not general workflow automation, but it illustrates the broader economic value of reducing slow, manual security response. See IBM’s Cost of a Data Breach research.

What healthcare compliance automation looks like in Zenphi
For healthcare organizations centered on Google Workspace, the operational challenge is often not a lack of applications. Work already moves through Gmail, Drive, Forms, Sheets, Calendar, Chat, Google Admin, an EHR or practice-management system, and one or more business applications. The compliance risk appears in the handoffs between them.
Governed healthcare workflows built around Google Workspace
Zenphi is designed for organizations that need to automate processes across Google Workspace while keeping approvals, access controls, PHI handling, and workflow history governed. A Business Associate Agreement is available on paid plans, and the healthcare solution combines Google Workspace-native actions with external systems through integrations and APIs.
Compliance improved by removing fragmented manual handoffs
CIT Clinics adopted Zenphi to connect Google Workspace and Zoho CRM under a HIPAA-compliant automation environment. Patient intake, Drive folder creation, charting spreadsheets, record updates, care-team database management, and applicant-review workflows were standardized instead of being coordinated through repetitive manual entry.
The goal is not to automate human accountability out of compliance. It is to make human judgment appear at the right point in the process — while the repetitive work around that judgment happens consistently and leaves evidence behind.